Site-to-Site VPN, Secure by Default
Connect your corporate network, remote offices, and cloud networks with encrypted tunnels.
 The #1 Business VPN
Trusted by 20,000+ organizations for over two decades.












Connect your corporate network, remote offices, and cloud networks with encrypted tunnels.
The #1 Business VPN
Access Server lets you connect a variety of networks and create secure site-to-site connections in addition to quickly and easily managing users, permissions, subnets, and connections with or without Linux knowledge.
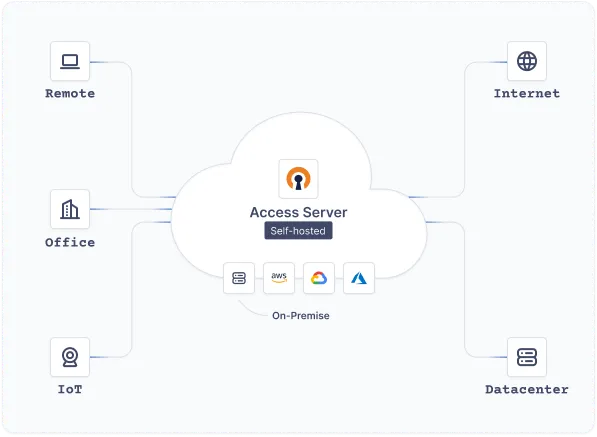


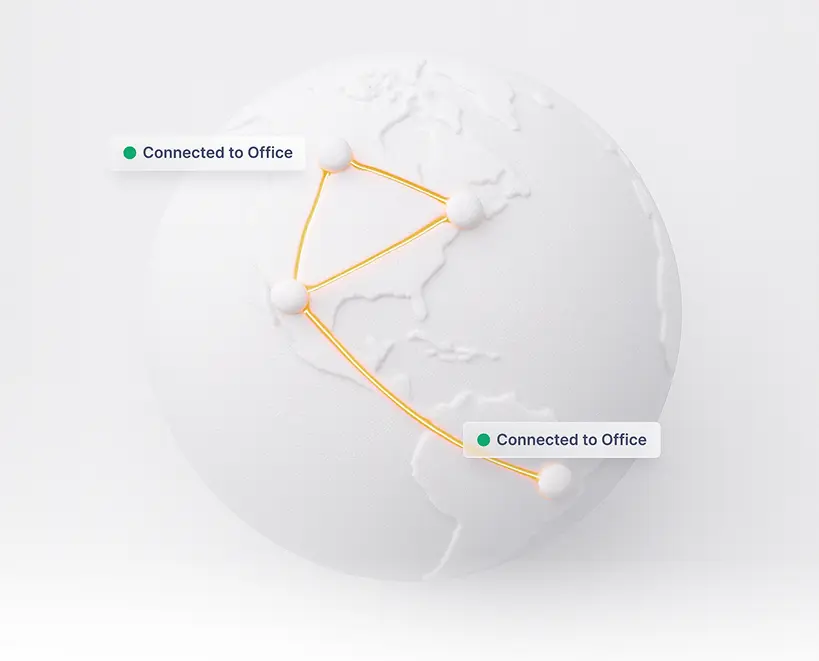
Our cloud VPN helps you quickly and easily set up a secure full-mesh network that connects your headquarters, remote offices, and cloud-based private networks to each other.
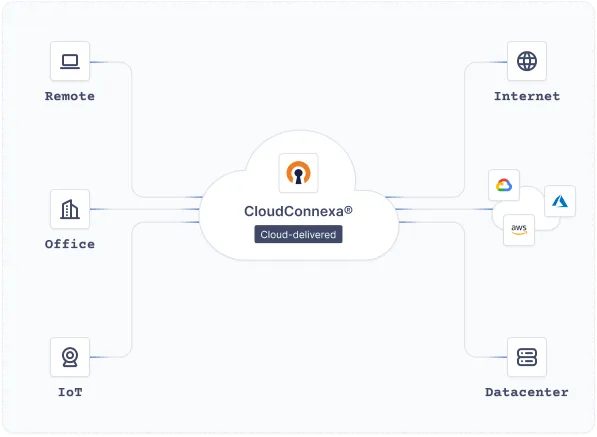


Most site-to-site VPNs stop at the tunnel: once headquarters, a branch office, and a VPC are connected, the networks implicitly trust each other, and any device on one side can typically reach any resource on the other. That is full network-to-network trust — the opposite of Zero Trust’s “never trust, always verify” model, and it means a single compromised laptop at one branch can become a path into every other connected location.
CloudConnexa closes that gap. The same Zero Trust Network Access (ZTNA) principles that govern individual user access also govern site-to-site traffic. For example, Access Groups apply to network-to-network connections, not just user-to-application ones, so you define exactly which applications and IP services each site is allowed to reach on the others — nothing more.
Connecting two of your own sites doesn't grant blanket access between them; each connection is governed by policy.
Access Groups scope precisely which resources and services are reachable between sites, replacing all-or-nothing LAN-to-LAN trust.
If one location is compromised, Zero Trust segmentation stops an attacker from moving freely into every other connected site or VPC.
This is the same Zero Trust Network Access (ZTNA) architecture behind CloudConnexa's remote-access and application-access controls, extended to your WAN. See how it all fits together on our Zero Trust Network Access (ZTNA) use case page.

Easy to configure options, add users, and that it has two factor authentication built in. You can configure the system to allow connections on common ports so that you're able to connect from pretty much anywhere in the world.

Configuring and updating my own server is super simple. In my experience, I've always had some difficulty setting up hardware VPN appliances, but OpenVPN was no-nonsense.

The OpenVPN Access Server AMI is a great out of the box VPN solution for your AWS VPC...

OpenVPN offers users a very simple and secure VPN option that is both economical and quick to install. Users are able to easily install it on their client devices.

The availability of client software for all operating systems and mobile devices means my customers can connect regardless of their setup.

Excellent, flexible solution for our Azure environment.
 SOC 2 Type 2
 ISO/IEC 27001:2022
 HIPAA Compliant
 GDPR Compliant

Compare products
Not sure which product is right for you? Check out our product comparison.
Read More
Secure Access Trends Report
Enterprise Strategy Group has compiled the trends in remote access you need to know.
Read More