Trusted by 20,000+ organizations
for over two decades.
What is the difference between OpenVPN and Palo Alto Networks?
OpenVPN delivers the secure access, Zero Trust, and identity integration you need — without platform complexity — get faster setup, simpler management, and pricing built for SMB growth.
Zero Trust Network Access (ZTNA): Built on Your VPN, Not Instead of It
Palo Alto Prisma Access is Palo Alto Networks' cloud-delivered SASE (Secure Access Service Edge) platform which requires full platform adoption to access ZTNA.
CloudConnexa and Access Server deliver ZTNA principles, such as continuous identity verification, device posture checks, and least-privilege access that blocks lateral movement, on top of the secure VPN foundation your team already trusts and already knows how to run.
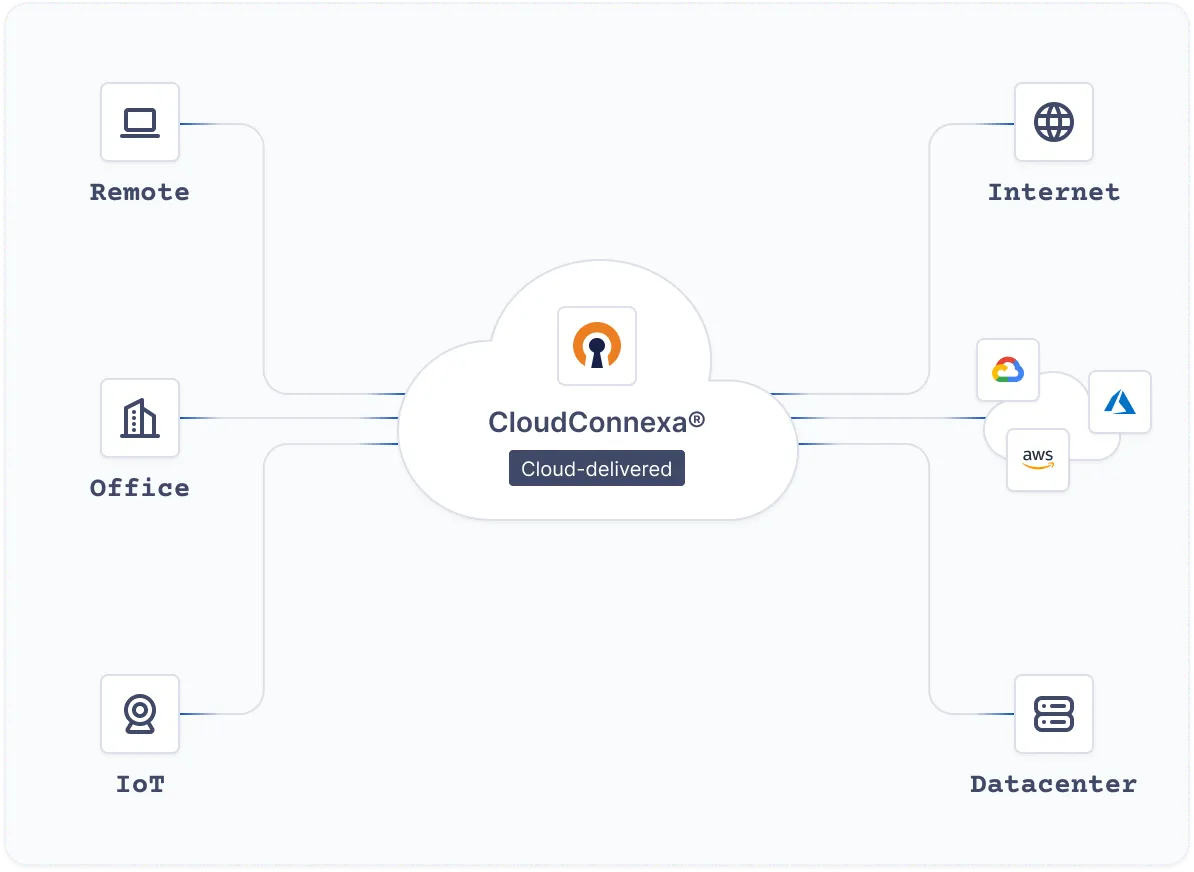
OpenVPN is one of the few vendors that delivers Zero Trust Network Access through both a cloud-delivered service (CloudConnexa) and a self-hosted solution (Access Server), backed by 20+ years of secure networking expertise, 90M+ downloads, and roughly 20,000 business customers worldwide.
What this looks like in practice:
Never trust, always verify
Identity- and context-based access policies defined per application, not per network segment.
Prevent lateral movement
CloudConnexa's Zero Trust Application Broker mediates the traffic between the user's device and applications via stand-in IPs scoped to a single authorized app, so there's no route into the private network to allow lateral movement.
Deploy your way
Cloud-delivered (CloudConnexa) or self-hosted (Access Server). Prisma Access ships as a cloud-delivered SASE platform only.
Transition on your timeline
Legacy applications can keep using VPN-level access while modern applications move to ZTNA, instead of a single forced cutover.
Palo Alto Networks Prisma Access is ideal for large enterprises with global operations, deep IT resources, and high budgets. But for SMBs and service providers, it ’s often too complex and expensive.
OpenVPN delivers the right balance of Zero Trust security, scalability, and cost-effectiveness — without enterprise-level complexity that is tied to a platform solution.
OpenVPN is a point solution purpose-built
OpenVPN is purpose-built for SMBs and MSPs, offering enterprise-grade security without enterprise-level overhead — setup takes less than an hour with no specialized infrastructure or complex integrations.
Palo Alto Prisma Access is best suited for large organizations with dedicated security teams and budgets; deployments require advanced expertise and integration across its broader ecosystem, slowing down time-to-value.
Flexible authentication options
OpenVPN supports SAML, LDAP, and local authentication, giving SMBs flexibility across modern and legacy environments.
Palo Alto focuses on integration within its own ecosystem, which can limit flexibility for smaller organizations.
Scalable, cost-efective growth
OpenVPN provides unlimited scalability with no bandwidth restrictions and multi-tenant management for MSPs.
Palo Alto's pricing and licensing structure are enterprise-grade — often too expensive and rigid for SMBs.
Cost Effective Scalability
OpenVPN adds Cyber Shield (IDS/IPS + content filtering) as a built-in, easy-to-use security layer.
Palo Alto offers advanced features like sandboxing and malware analysis — but at higher cost and complexity.
Backed by enterprise-grade security
SOC 2 Type 2
ISO/IEC 27001:2022
HIPAA Compliant
GDPR Compliant
Two solutions —
one goal
Self-hosted or cloud-delivered: We've got your network security covered.
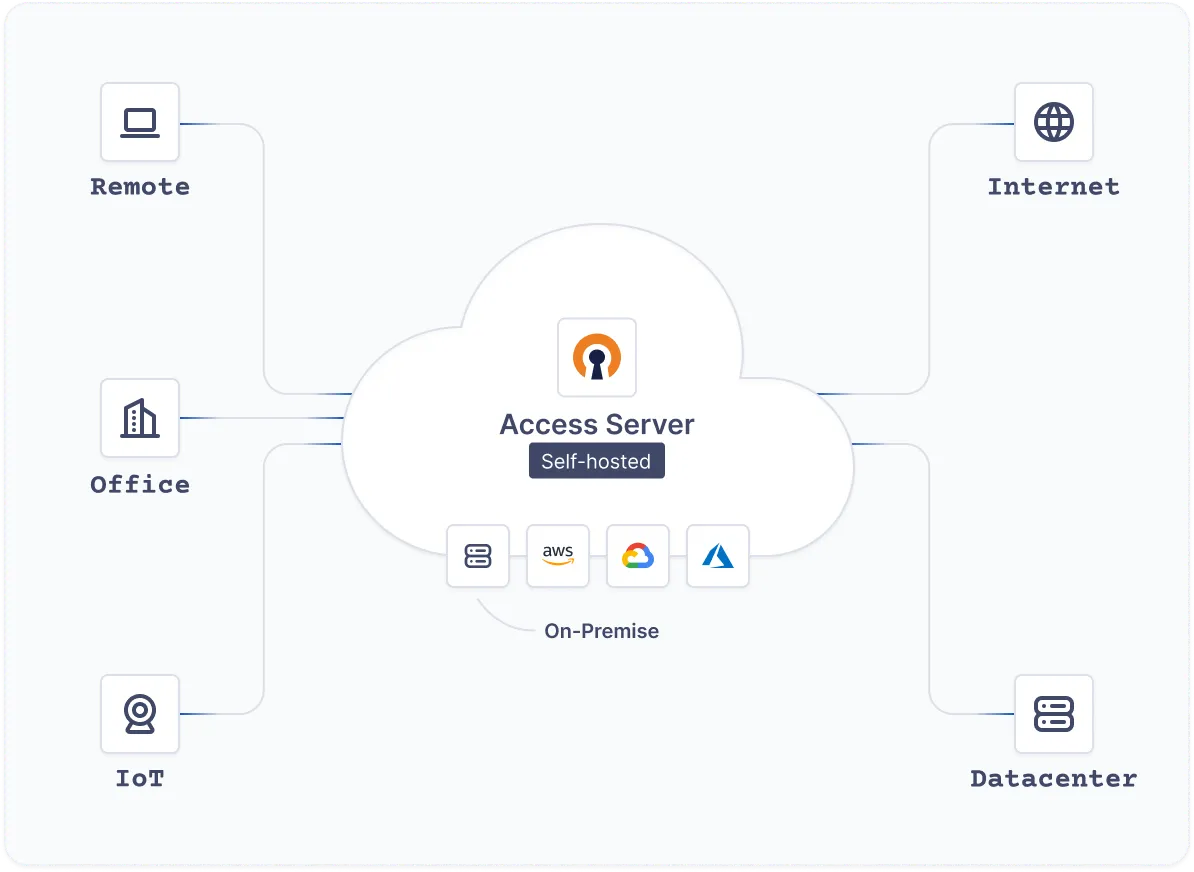
Self-hosted
Access Server
Access Server gives you complete control over your security architecture with customizable access policies and private tunneling.
Deploy on IaaS providers, Docker, Linux, Hyper-V, and VMware ESXi
Get started fast with a ready-to-use templates
Protect your data by routing internet traffic through the Access Server
Enforce access policies with identity, device, and IP verification
Easy to configure options, add users, and that it has two factor authentication built in. You can configure the system to allow connections on common ports so that you're able to connect from pretty much anywhere in the world.
Johnathan B.Surry Telephone
Configuring and updating my own server is super simple. In my experience, I've always had some difficulty setting up hardware VPN appliances, but OpenVPN was no-nonsense.
Alex H.DGDean
The OpenVPN Access Server AMI is a great out of the box VPN solution for your AWS VPC...
John G.Anovys, LLC
OpenVPN offers users a very simple and secure VPN option that is both economical and quick to install. Users are able to easily install it on their client devices.
Jeremy F.Intelligent Pathways
The availability of client software for all operating systems and mobile devices means my customers can connect regardless of their setup.
Josh Wc.nexgen|packaging, LLC
Excellent, flexible solution for our Azure environment.
Implement Zero Trust without starting from zero
Join thousands of organizations that trust OpenVPN for secure, high-performance remote access that adapts to your business — not the other way around.
A Virtual Private Network (VPN) provides your business with a securely encrypted internet connection (or "tunnel") to securely connect devices to business assets over otherwise unsecured networks. VPNs, like OpenVPN, work by masking your IP address and encrypting your internet traffic. VPN protection is an important piece of a layered security protocol that's essential to protecting company data as well as an employee's personal data. Using a VPN service gives you the ability to remotely access important network resources and connect your company's branches and locations worldwide. A zero trust VPN offers the tenets of zero trust built on the solid foundation of a VPN.
A Zero Trust VPN uses a VPN as the foundation of zero trust network access. Access Server and CloudConnexa can be used to implement a zero trust network access solution that secures your network resources while limiting access to only what is necessary.
According to Gartner, "Zero trust network access (ZTNA) is a product or service that creates an identity- and context-based, logical access boundary around an application or set of applications." Doing this hides the apps from discovery and restricts access using a trust broker and a set of named entities. The broker verifies users based on identity, context, and policies — and stops lateral movement in the network. Because application assets are removed from public visibility, potential attack surface is reduced.
ZTNA also relies on least privilege access, which means that employees should only have access to the programs and applications that are necessary to do their jobs. Using a VPN, you can enforce the tenets of ZTNA and build the foundation for the principle of least privilege.
Yes. CloudConnexa and Access Server both deliver Zero Trust Network Access (ZTNA) capabilities — identity- and context-based access policies, continuous verification, and lateral-movement prevention — built on the OpenVPN tunneling protocol.
Prisma Access is a cloud-delivered SASE (Secure Access Service Edge) platform built to replace traditional VPN infrastructure entirely. OpenVPN takes a different approach: Zero Trust Network Access is layered on top of the VPN foundation you already have, so legacy and modern applications can move to ZTNA on your own timeline instead of all at once.
Yes. Unlike Prisma Access, which is only available as a cloud-delivered SASE platform, OpenVPN offers ZTNA through either CloudConnexa (cloud-delivered) or Access Server (self-hosted) — so you're not locked into a single deployment model or a full platform migration.
OpenVPN has transparent, flexible pricing that fits all budgets. Starting at just $7 per connection per month, you can see a customized price based on your business size here.
You can cancel your subscription at any time and unused funds will be credited to your account for future usage. For refunds, contact sales@openvpn.net.
 The #1 Business VPN